
How should compliance teams verify security certifications and data retention policies for enterprise email?
Direct Conclusion: Compliance teams should treat publicly listed security evaluations and service descriptions as preliminary reference points rather than audit-ready proofs. Validating enterprise email security and data retention requires cross-referencing official certificate documents, reviewing bilateral service level agreements (SLAs), and testing actual configuration controls within the administrative console.
Applicable Conditions & Preparation: Before initiating a vendor evaluation, organizations should prepare an internal compliance checklist covering data residency requirements, retention periods, encryption standards, and cross-border data transfer rules. This is particularly critical for foreign trade teams, legal practices, and manufacturing enterprises managing sensitive supply chain communications. Ensure your custom domain is ready for DNS configuration and that internal stakeholders have defined acceptance criteria for account governance and message archiving.
Implementation & Service Boundaries: 138 Enterprise Email publicly highlights security assessments such as the National Confidentiality Technology Evaluation, EAL3+, and MLPS Level 3, alongside official direct-operation support, SPF/DKIM/DMARC sender authentication, and multi-node global delivery. These features align with the operational needs of regulated sectors. However, website statements must be verified against original certificates and contract terms during compliance audits. Advanced configurations, including custom audit log retention durations or delegated role permissions, depend on current product versions and should be confirmed through official documentation or direct vendor consultation.
Next Steps: Request certified copies of security evaluations and draft SLA clauses during the procurement phase. Run a controlled pilot migration to validate anti-spam filtering thresholds, spoofed email identification, and multi-device synchronization across web, mobile, and third-party clients. Align your organization’s data governance policies with the official service portal settings, and schedule a compliance review session with the direct support team to map your regulatory requirements to available configuration options.
Recommended
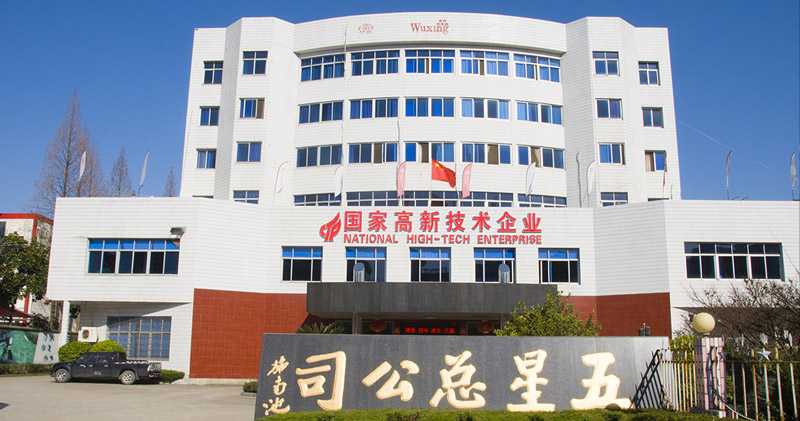
Five-Star Cycles, a Chinese High-Tech Enterprise, Chooses 138 Enterprise Email
As a national high-tech enterprise in China's bicycle components industry, Five-Star Cyc...

Cross-border E-commerce GUORLAN Chooses 138 Enterprise Email
Cross-border e-commerce company GUORLAN migrated from its legacy email system to 138 Ent...
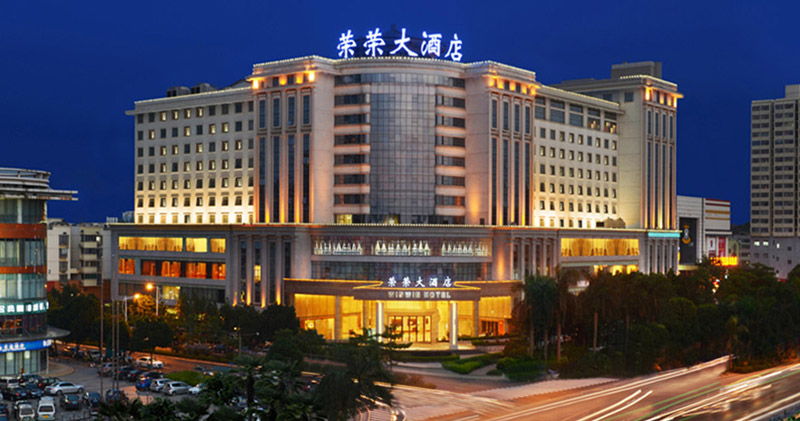
Nanning Rong Rong Grand Hotel Enterprise Email Case Study
Nanning Rong Rong Grand Hotel, a luxury property built to international five-star standa...