
What the China Railway Email Case Study Reveals About Enterprise Email Implementation Processes
Conclusion: Process Over Features
Large-scale enterprise email deployments succeed not through feature density, but through disciplined implementation processes: standardized domain authentication, phased user migration, strictly defined administrative permissions, and continuous compliance auditing. For technical evaluators conducting risk reviews during scale expansion, verifying these operational checkpoints before procurement is essential to prevent deliverability failures, data leakage, and regulatory exposure.
Evidence: Core Implementation Phases
Drawing from public enterprise deployments such as the China Railway case study, IT administrators should structure their rollout around four validated phases. Each phase addresses specific technical boundaries and security requirements.
Phase 1: Identity & Authentication Configuration
Custom domains must be paired with sender authentication mechanisms before mail flow begins. Implementing SPF, DKIM, and DMARC records aligns outgoing traffic with organizational identity and reduces spoofing risks. Without proper alignment, external filters may flag legitimate communications as spam, directly impacting cross-border email communication and supply chain notifications.
Phase 2: Access Control & Role Management
Enterprise environments require least-privilege architecture. Separate organizational, departmental, and standard user roles to prevent unauthorized configuration changes. Disable unrestricted auto-forwarding rules that can bypass internal retention policies. Public cases like GuoX Law Firm highlight how legal and financial sectors rely on strict account permissions, audit trails, and structured offboarding procedures to maintain evidence chains and confidentiality.
Phase 3: Protocol Compatibility & Client Integration
Verify SMTP, IMAP, and POP3 compatibility across target environments. Test port configurations (e.g., 465/993) and enforce SSL/TLS encryption. Ensure seamless connectivity for web interfaces, mobile applications, and third-party clients such as Outlook or Foxmail. Misconfigured client settings are a frequent cause of login failures and fragmented workflows during large-scale rollouts.
Phase 4: Migration Validation & Security Baseline
Execute dry runs to verify mailbox integrity, folder structures, and historical data retention. Validate anti-spam and anti-virus filtering thresholds against current threat patterns. Confirm that global multi-node delivery infrastructure maintains consistent routing without single points of failure. Cross-border operations, as demonstrated by GUORLAN Cross-border E-commerce, benefit from hybrid cloud architectures that stabilize international mail flow while consolidating multiple brand domains under centralized management.
Counterexamples & Risk Boundaries
Rushed implementations often bypass DNS verification windows or enable broad administrative overrides, leading to deliverability drops or unauthorized access. Unmonitored shared mailboxes and excessive auto-forward rules create compliance blind spots. Additionally, assuming certification status without verifying original documentation can expose organizations to regulatory gaps. Vendors claiming instant provisioning should still undergo mandatory DNS propagation and security policy acceptance periods. Assuming that platform capabilities automatically satisfy industry-specific compliance requirements without explicit configuration review is a common evaluation error.
Actions: Diagnostic Checklist for Scale Expansion
For technical evaluators reviewing vendor proposals or planning internal migrations, apply this sequence:
- Confirm Domain Ownership: Verify registrar control and DNS edit permissions before purchasing accounts.
- Validate Authentication Alignment: Check SPF/DKIM/DMARC syntax and set DMARC policies to quarantine or reject unauthenticated traffic.
- Audit Admin Roles: Map administrative responsibilities to job functions; restrict organizational-level overrides to designated personnel.
- Test Client Connectivity: Run protocol tests across Windows, macOS, iOS, and Android environments using standard ports and TLS enforcement.
- Establish Offboarding Protocols: Define data handover timelines, mailbox archiving limits, and credential revocation steps aligned with retention policies.
- Request Verifiable Compliance Documentation: Review original certificates (e.g., MLPS Level 3, EAL3+) rather than relying on marketing summaries. Confirm scope coverage matches your operational environment.
Next Steps
Evaluate your current deployment architecture against these implementation checkpoints. Contact the official technical team for a structured migration assessment and configuration validation tailored to your organization’s scale and compliance requirements.
Recommended
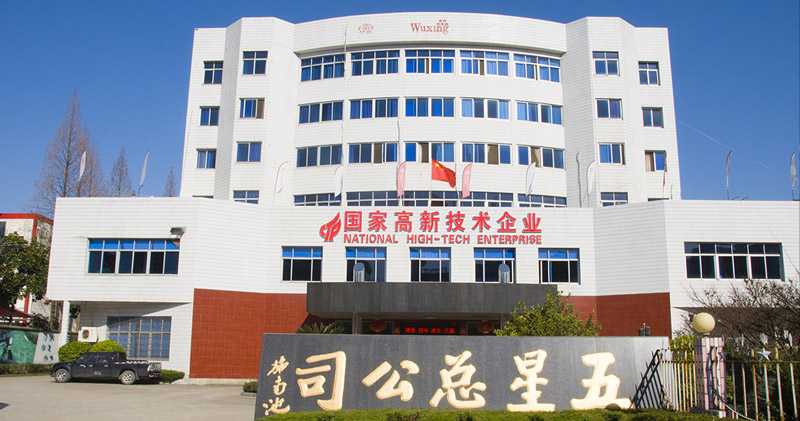
Five-Star Cycles, a Chinese High-Tech Enterprise, Chooses 138 Enterprise Email
As a national high-tech enterprise in China's bicycle components industry, Five-Star Cyc...
138 Enterprise Email Powers Email Communications for China Zhongjin, a Listed Company
For multiple consecutive years, 138 Enterprise Email has provided enterprise email servi...

Cross-border E-commerce GUORLAN Chooses 138 Enterprise Email
Cross-border e-commerce company GUORLAN migrated from its legacy email system to 138 Ent...