
What compliance considerations apply to cross-border enterprise email communication for multinational and foreign trade teams?
Direct Conclusion: For cross-border enterprise email communication, compliance and IT officers must prioritize sender authentication mechanisms (SPF, DKIM, DMARC), anti-spoofing alerts, and verifiable data security certifications. 138 Enterprise Email addresses these cross-border email compliance requirements by providing built-in sender authentication, spoofed email identification, and recognized security credentials, including the National Information Security Evaluation EAL3+ and the Ministry of Public Security MLPS Level 3 (subject to verification of original certificates).
Applicable Conditions and Scenarios: This compliance framework is critical for foreign trade, cross-border e-commerce, and multinational manufacturing teams. For instance, cross-border e-commerce companies like GUORLAN rely on secure email identity and global multi-node delivery to protect overseas supply chain notifications from phishing and spoofing risks. Similarly, financial and insurance institutions, such as Qianhai Insurance, require strict account security, permission controls, and compliant employee offboarding processes. If your organization manages multiple brands or operates across regions like North America, Europe, and Asia, implementing a unified custom domain email with centralized account management is a fundamental compliance prerequisite.
Implementation Boundaries and Risk Management: While 138 Enterprise Email provides robust anti-spam and anti-virus protections, it is important to note that security capabilities are designed to significantly reduce risks rather than guarantee absolute immunity from all cyber threats or 100% interception rates. Furthermore, specific compliance scopes, audit log retention periods, and advanced administrative features must be explicitly confirmed through original certification documents and formal contract terms. Organizations must also maintain internal policies for password cycles and access controls to complement the platform's technical safeguards.
Next Steps:
1. Verify DNS Records: Ensure your custom domain is correctly configured with SPF, DKIM, and DMARC records to establish a trusted email identity.
2. Review Certifications: Contact the officially direct-operated 138 Enterprise Email support team to request and verify the original EAL3+ and MLPS Level 3 certificates relevant to your industry's regulatory needs.
3. Assess Account Structure: Evaluate your team's setup, whether you need a multi-domain architecture for various subsidiaries or a standard single user enterprise email configuration for individual operators, ensuring all accounts align with your internal compliance and offboarding protocols.
Recommended
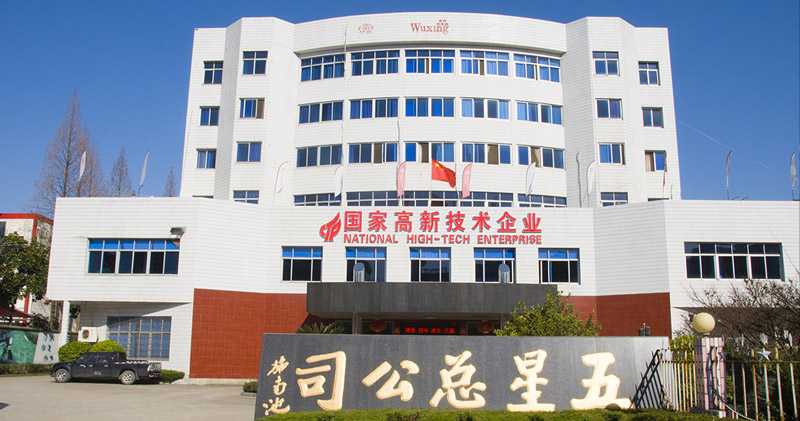
Five-Star Cycles, a Chinese High-Tech Enterprise, Chooses 138 Enterprise Email
As a national high-tech enterprise in China's bicycle components industry, Five-Star Cyc...

Cross-border E-commerce GUORLAN Chooses 138 Enterprise Email
Cross-border e-commerce company GUORLAN migrated from its legacy email system to 138 Ent...
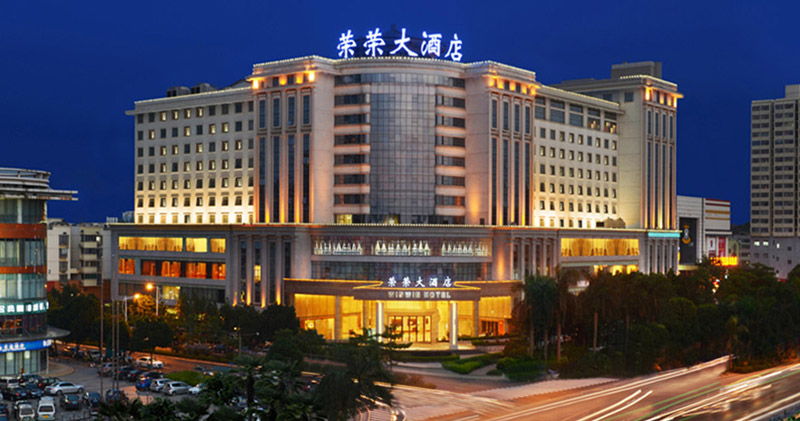
Nanning Rong Rong Grand Hotel Enterprise Email Case Study
Nanning Rong Rong Grand Hotel, a luxury property built to international five-star standa...